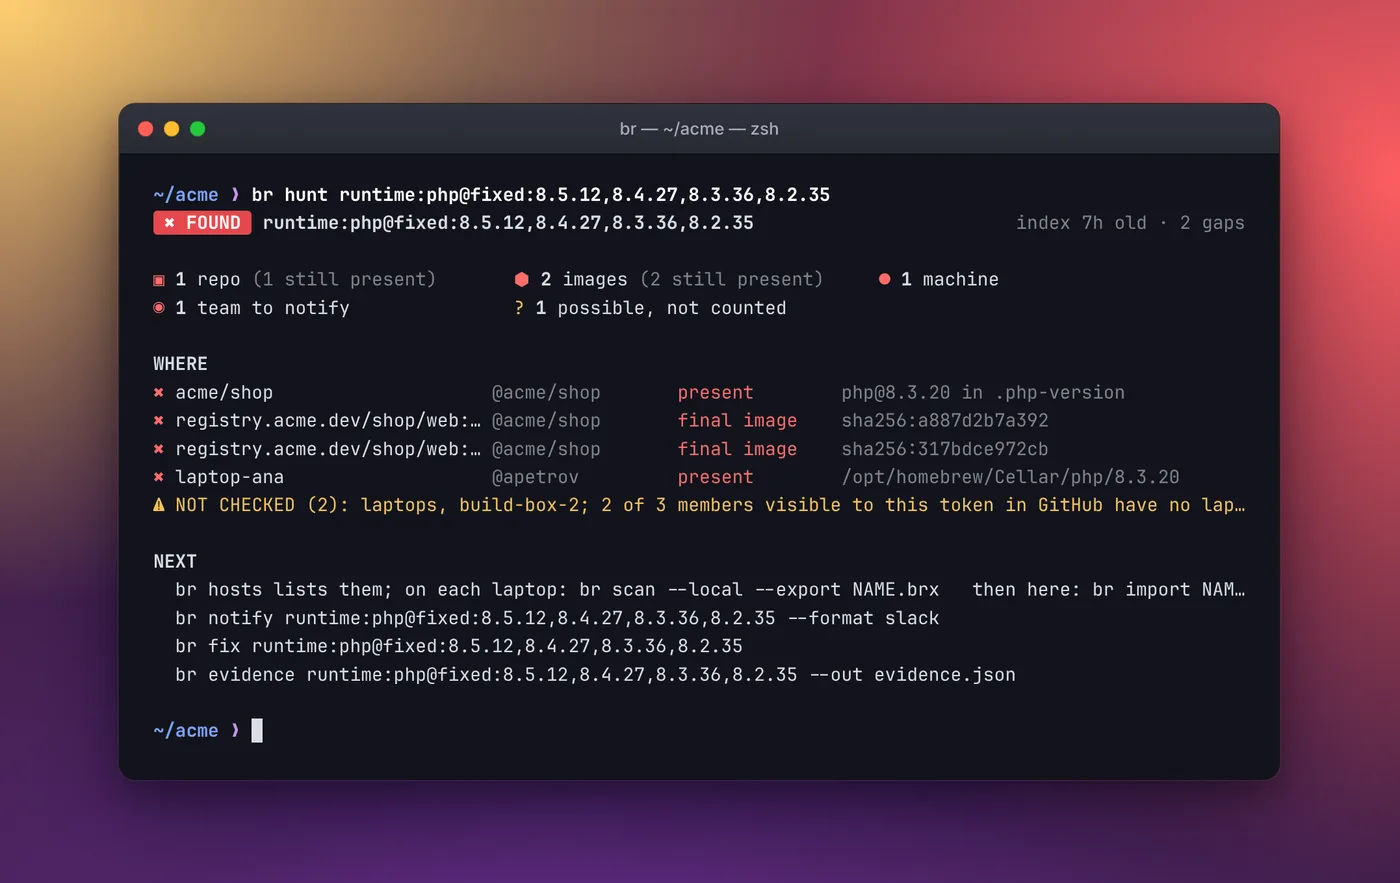
 Critical
PHP2Shell
Remote code execution in PHP itself. Every PHP below the fixed release of its line, in version files, Dockerfiles, workflows, images and machines.
$ br hunt runtime:php@fixed:8.5.12,8.4.27,8.3.36,8.2.35Open source CLI · read-only
br
Repos, CI runs and the secrets they held, caches, container images (deleted layers included) and laptops. Then who owns each place and how to clean up. It runs on your machine and only reads.
$ npx -y @jondot/blastradius demoNo token yet? br demo runs a made-up incident on a sample org built into the binary.
What you see
Each falling bug is a real advisory. br checks it on the way down, or shows where it landed in your org. Click the sky to check one yourself, then scroll down through the layers br reads.
One command
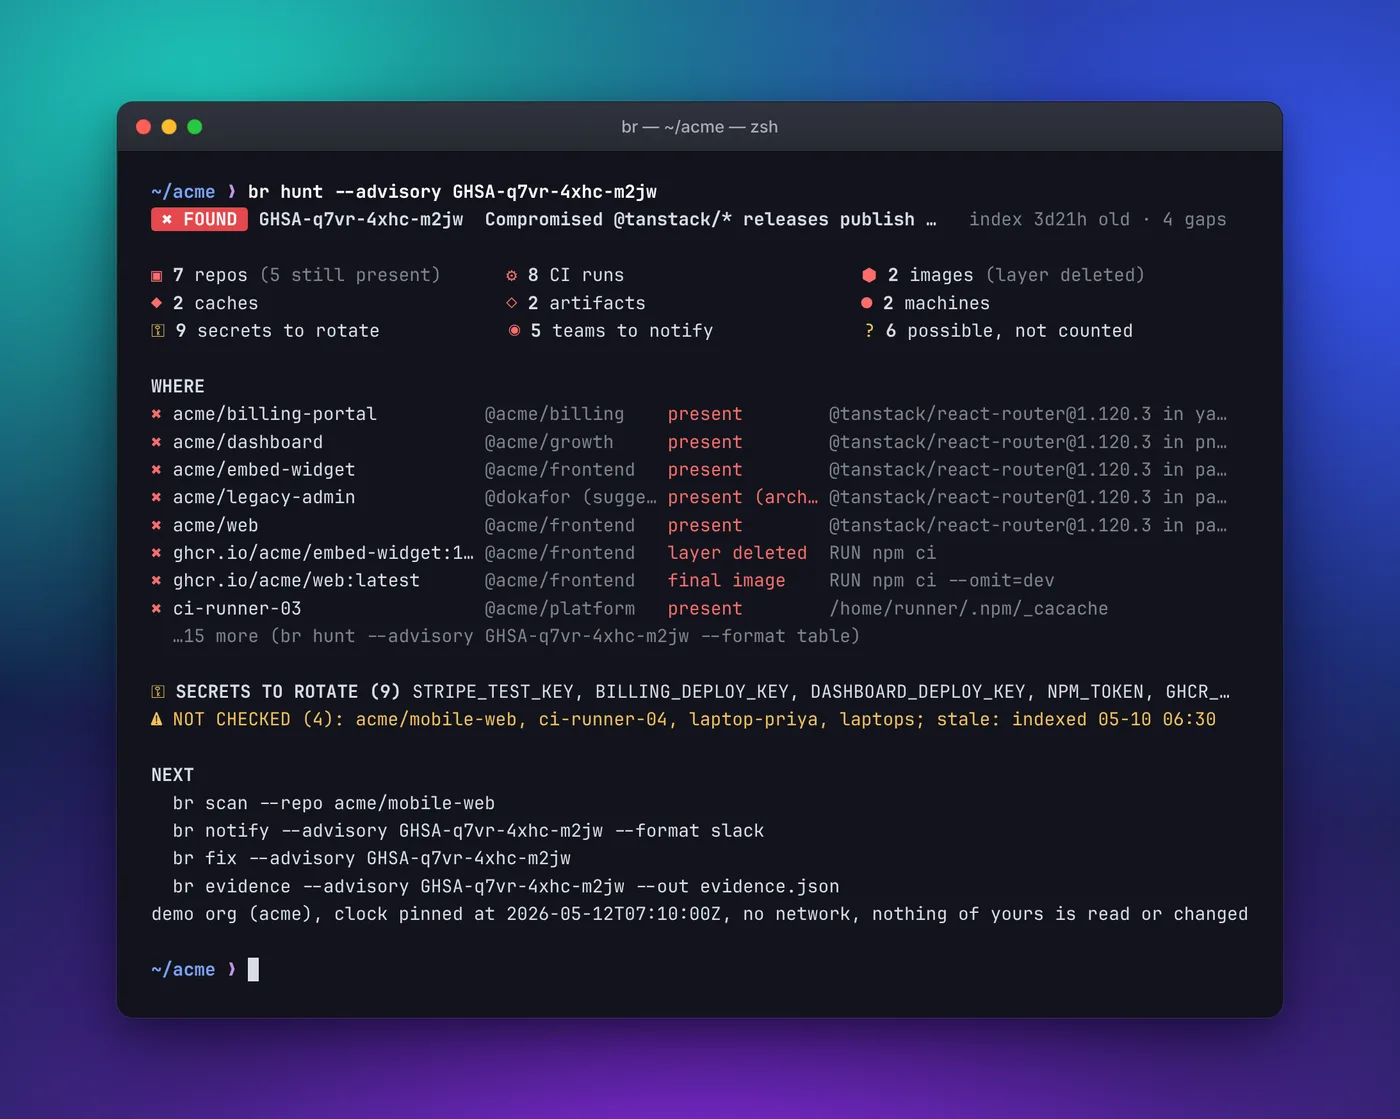
Not just packages
Four incidents landed in a few days, and none was a bad package version. Each one is a single br hunt. Screenshots are real runs against a sample org, with made-up names and certificates.
CriticalRemote code execution in PHP itself. Every PHP below the fixed release of its line, in version files, Dockerfiles, workflows, images and machines.
$ br hunt runtime:php@fixed:8.5.12,8.4.27,8.3.36,8.2.35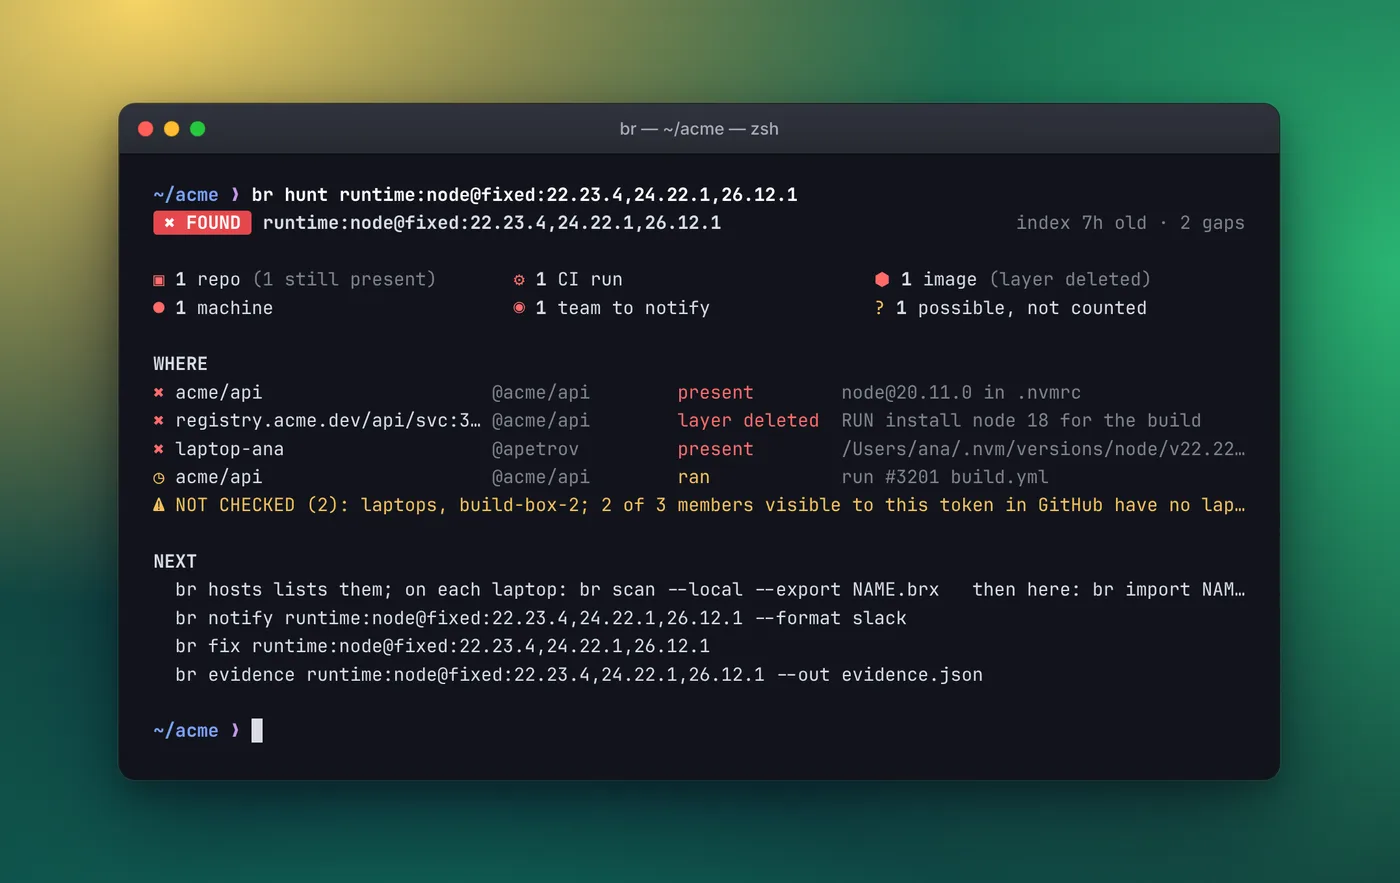 High
Images, runners and laptops on a Node line below the fix, and end-of-life lines that got none.
$ br hunt runtime:node@fixed:22.23.4,24.22.1,26.12.1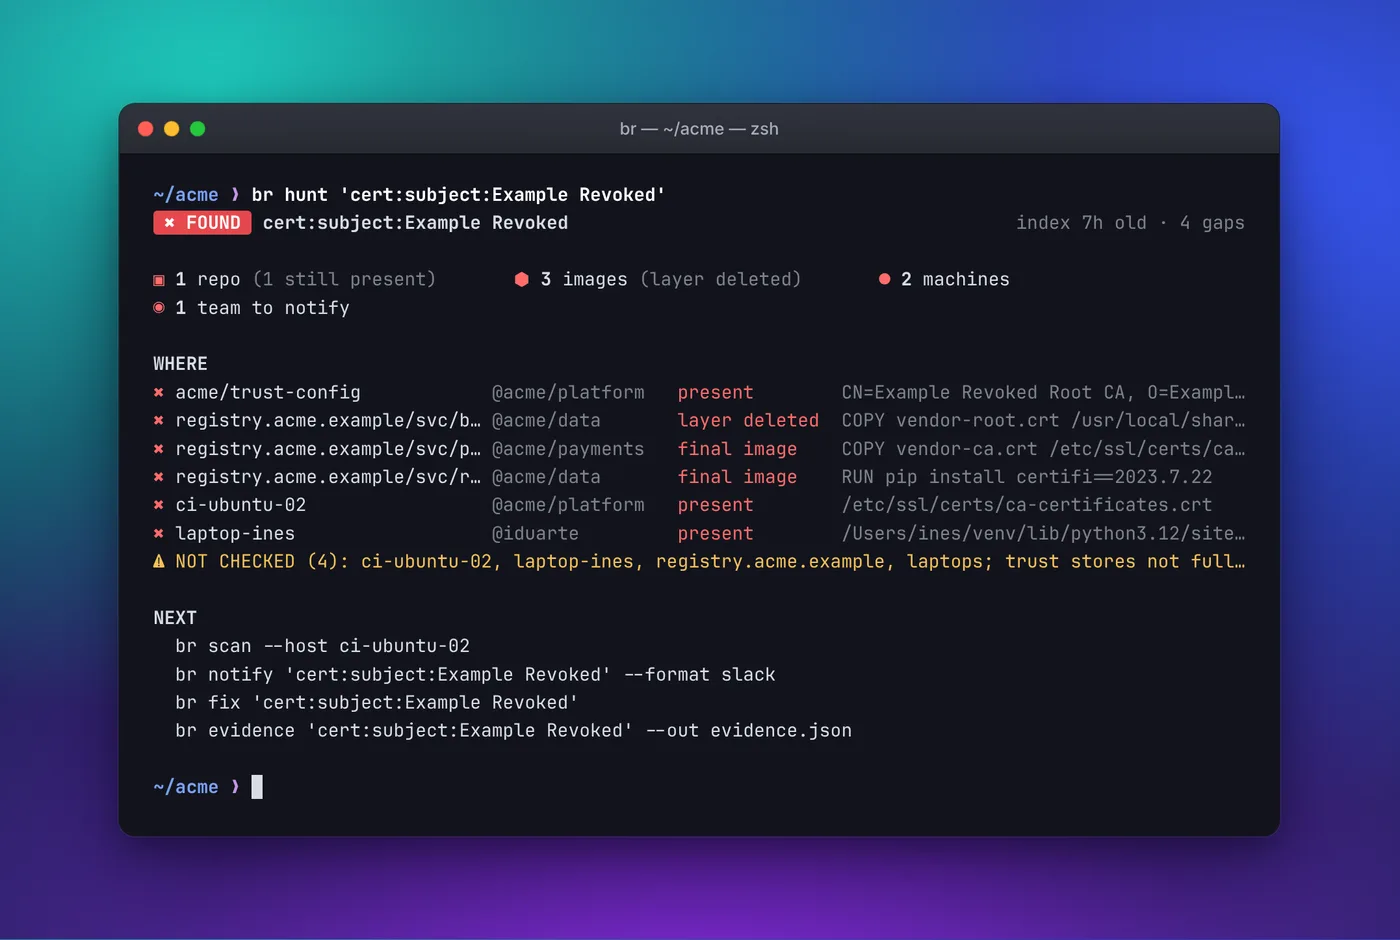 High
OS bundles in image layers, certifi, Java cacerts and PEM files in repos that still trust it.
$ br hunt "cert:subject:emSign ECC Root CA - G3"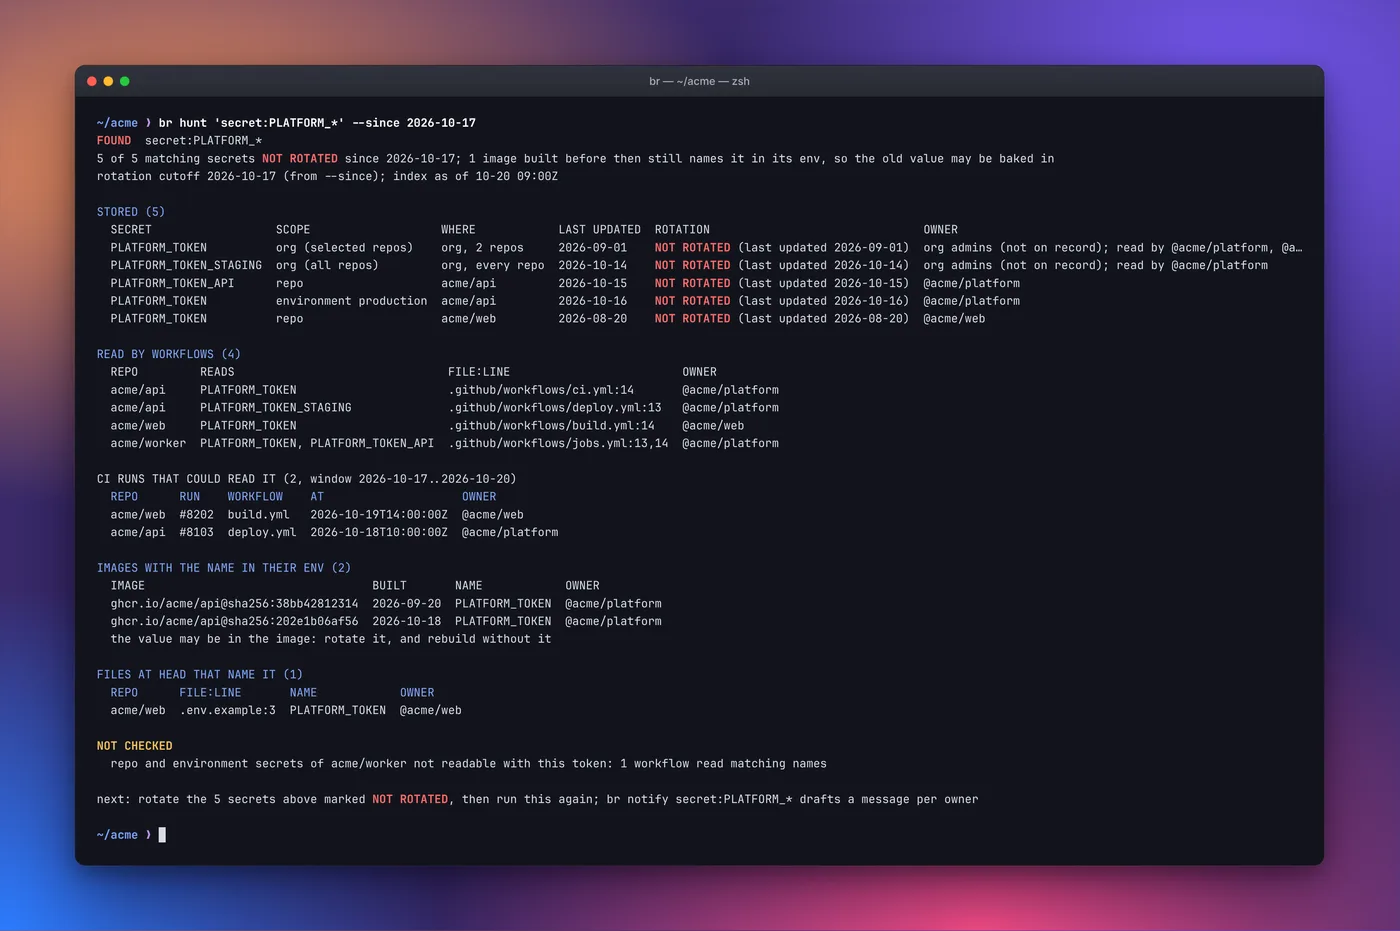 Critical
Where each matching secret is stored, what read it, and whether it was rotated since. From names and dates only; br never reads a secret value.
$ br hunt 'secret:RAILWAY_*' --since DATEWhere it looks
Built once from your GitHub org, your container registries and the machines you point it at. Laptops that can't be reached scan themselves and send a sealed file.
Published today
The same bugs that fall at the top of this page: the most severe of the latest reviewed advisories on GitHub. Each row is one command against your index.
| Advisory | Package | Summary | Command |
|---|---|---|---|
| Loading… | |||
Where br fits
| Tool | Question it answers | Output |
|---|---|---|
| Dependabot, osv-scanner, trivy | Is a known-vulnerable package in this code or image now? | Alerts, PRs, scan reports |
| Socket | Does this package behave badly, before I install it? | A verdict on a package |
| GitHub secret scanning | Has a secret been committed? | Alerts |
| br | A thing is known to be bad. Where did it go, what could it reach, is it really gone? | Places, CI runs and secret names, owners, a sealed record |
Trust
--now, --live or --path.Exit codes
| 0 | Clear |
| 10 | Found |
| 3 | Clear with gaps, under --strict |
| 5 | No index, or a stale one |
| 11 | Nothing found, under --fail-if none |
| 4 2 1 | Auth problem, usage error, failure |
Install
$ npm i -g @jondot/blastradius               # Node 18+; or the installer below
$ br demo                                    # try it on a sample org, no token
$ br init --org YOUR_ORG                     # once, with a read-only token
$ br hunt --advisory GHSA-xxxx-xxxx-xxxx
Without Node, the installer checks the sha256 and puts br in ~/.local/bin:
$ curl -fsSL https://raw.githubusercontent.com/jondot/blastradius/main/install.sh | shLinux, macOS and Windows builds are on the releases page.